
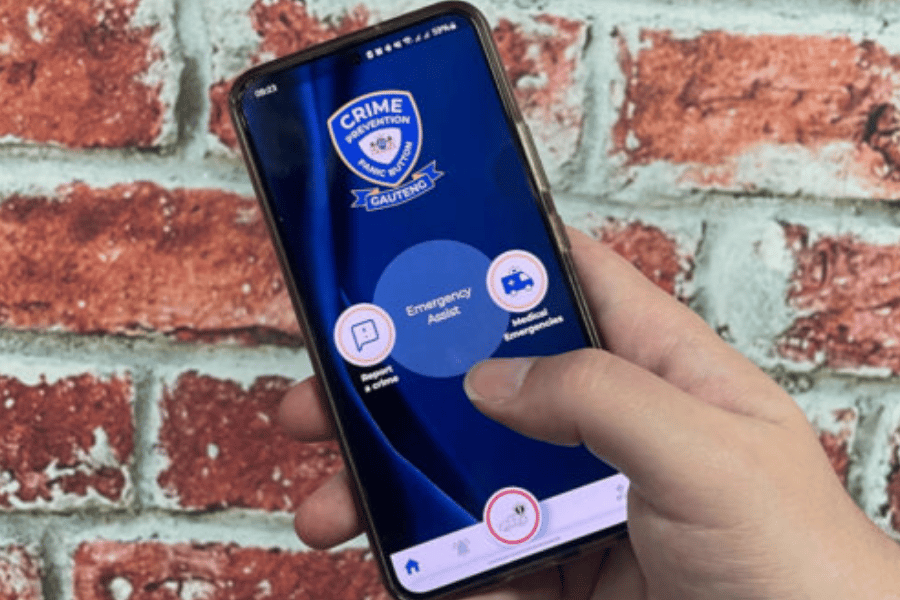
The Democratic Alliance (DA) will report a major data breach involving the Gauteng Provincial Government’s e-Panic Button app to the Information Regulator of South Africa.
The party says it wants the regulator to investigate a possible violation of the Protection of Personal Information Act (POPIA), including how the sensitive information of crime victims was exposed, how the Department of e-Government responded, and whether affected residents were notified.
According to the report, the app’s system exposed the names and personal details of people who reported crimes, along with the contents of their reports, photographs, GPS coordinates, location histories, and even one-time PINs used to log into the application.
Among the information that could be accessed were reports relating to domestic violence and assault. Some of the exposed data reportedly dates back to the launch of the app in 2024.
The DA’s Gauteng spokesperson for e-Government, Michael Waters MPL, described the exposure as a serious failure by the department to protect residents who turned to the state for help in moments of crisis.
Waters said it was even more concerning that the department never informed the Gauteng Legislature’s Portfolio Committee on e-Government, which is responsible for oversight, about the security failure.
He said this is the second time highly sensitive information submitted to the Gauteng Provincial Government (GPG) has been exposed.
“The exposure of highly sensitive personal information belonging to Gauteng residents who used the provincial government’s e-Panic Button app represents a serious failure,” Waters said.
He added that according to media reports the vulnerabilities were not sophisticated and did not require advanced hacking skills to exploit. A tech-savvy computer user could have accessed the information.
The DA is now demanding that the department urgently appear before the Portfolio Committee to account.
The party wants answers on how long residents’ information was left exposed, whether it was accessed by unauthorised persons, and whether access logs have been independently examined.
Waters also questioned the department spending priorities, given its limited budget, asking whether it should be investing in e-Panic Buttons instead of strengthening its cybersecurity systems.
He warned that the breach undermines trust at a time when government is urging victims of violence to report crimes, and comes as Gauteng, particularly Ekurhuleni, is reeling from the recent deaths of 11 women amid South Africa’s ongoing gender-based violence and femicide crisis.
“Residents who report domestic violence, assault and other serious crimes must be able to trust that the information they provide to the government will be protected. Instead, a person reporting an alleged abuser could potentially have had their identity, location, movements, and crime report exposed,” Waters said.
He said a government that cannot protect personal information submitted electronically is putting the digital economy and job creation at risk, as residents and investors need confidence that cybersecurity systems are in place.
Waters said the GPG now owes every affected resident a full explanation of what happened, whether their information was accessed, what steps have been taken to protect them, and who will be held accountable.
“A DA-led Gauteng provincial government would protect sensitive information to ensure that victims are not exposed or made to suffer a double crisis,” he said.